Manage Enrolled Devices, Customers & Payment Operations from One Secure Workspace.
HeliumMDM gives authorized retailers a structured portal for Android and Apple enrollment, device lifecycle operations, customer KYC records, and installment workflows — with permission controls, activity history, and operational safeguards built into every critical action.
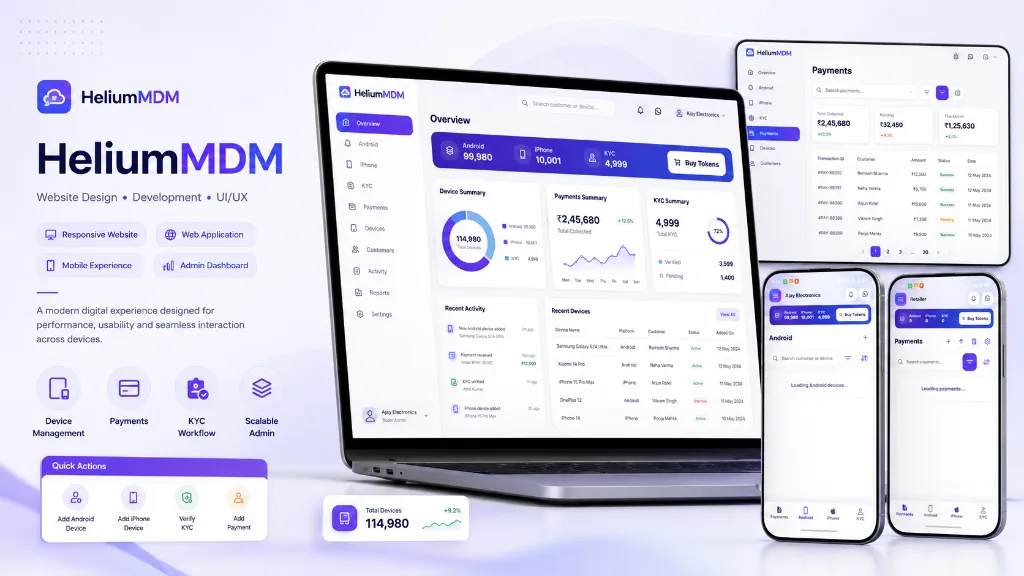
Four Independently Deployable Systems
HeliumMDM brings Android Enterprise/CDPC management, Apple device enrollment, customer onboarding, KYC records, and payment-mandate operations into one secured retailer portal (mdm.ehelium.in/dashboard).
HeliumMDM_iOS
Apple enrollment, DEP/ABM coordination, SCEP certificates, APNs check-in, management commands, and device lifecycle.
MySQL, NanoMDM, NanoDEP, SCEP
HeliumMDM_CDPC
Android Device Policy Controller enrollment, MQTT check-in, commands, device telemetry, retailer accounts, and unified portal.
PostgreSQL, Mosquitto, Redis
HeliumMDM_Payments
Mandates, installment schedules, signed provider webhooks, payment reconciliation, and unlock-only EMI automation.
MySQL mandate schema
HeliumMDM_Customers
Customer identity records, customer consent capture, KYC documents, and customer-device relationship mapping.
KYC tables in mandate schema
Phase 1 System Architecture Matrix
These are separate deployment and security boundaries even when the unified dashboard presents them as one seamless product.
| Product System | Operational Responsibility | Primary Data & Infrastructure |
|---|---|---|
HeliumMDM_iOS |
Apple enrollment, DEP/ABM coordination, SCEP certificates, MDM check-in, commands, and lifecycle | MySQL, NanoMDM, NanoDEP, SCEP state |
HeliumMDM_CDPC |
Android Device Policy Controller enrollment, MQTT check-in, commands, device status, retailer accounts, and unified portal | PostgreSQL, Mosquitto, Redis |
HeliumMDM_Payments |
Mandates, installment schedules, signed provider webhooks, reconciliation, and unlock-only EMI automation | Payments-owned MySQL mandate schema |
HeliumMDM_Customers |
Customer identity, consent, KYC capture, protected documents, and customer-device relationships | KYC tables in Payments-owned mandate schema |
Helium_WAAPI messaging development is deferred and outside this Phase 1 brief.
Public-Facing Positioning & Responsible Operations
HeliumMDM should be described as an authorized device-management and retailer-operations platform. It must never be presented as spyware, a consumer surveillance product, a guaranteed debt-recovery mechanism, or a substitute for lawful customer consent and retailer responsibility.
Dedicated Tracks for Distributed Hardware
Purpose-engineered agents and management protocols tailored to each operating system's native security boundaries.
Android Custom Device Policy Controller
Built specifically for dedicated enterprise endpoints, company-owned devices, and retail POS. Operates at the Android Device Owner layer with deep hardware and OS-level restrictions.
- QR-Code Zero-Touch Provisioning
- Single-App & Multi-App Kiosk Lock
- Silent APK Install & Update Delivery
- Real-time MQTT Push Telemetry
- Enterprise FRP (Factory Reset Protection)
- USB, Wi-Fi & Camera Restriction Toggles
Android DPC Security Policy Flow
└── DPC APK downloaded & set as DEVICE_OWNER
├── Lock Task Mode (Kiosk)
├── Disallow safe mode & factory reset
└── Push Wi-Fi & corporate certificates
└── Battery, GPS geofence, memory & network logs
iOS & iPadOS MDM Track
Engineered using Apple's official MDM protocol and NanoMDM backend services. Securely supervises iPhones and iPads across retail stores, classrooms, and enterprise teams.
- APNs (Apple Push Notification) Protocol
- Activation Lock Bypass Management
- Autonomous Single App Mode (ASAM)
- Configuration Profiles & Certificates
- Supervised Fleet Inventory & OS Telemetry
- Remote Lock & Erasure Workflows
Apple MDM Core Attributes
Windows Management Agent (Roadmap)
Extending Helium fleet governance to Windows laptops, point-of-sale workstations, and branch desktop systems. In active MVP development.
- Lightweight Windows Background Service
- Hardware & OS Inventory Audit
- Software Patch & Security Posture
- Remote Policy & Execution Dispatch
Unified Fleet Console
Admins can manage Android handhelds, iOS tablets, and Windows terminals side-by-side in one consolidated web dashboard.
Experience HeliumMDM Controls in Action
Toggle between policy scenarios to see how HeliumMDM governs organizational hardware. This is a simulation with sample data. Book a demo to see the real console.
Order #HL-9824 Ready for Payment
Amount: ₹14,999 • Customer Phone: +91 98*** 22100
How Much Time Could HeliumMDM Save Your Team?
Manual device enrollment, updates, troubleshooting, and asset audits add up. This illustrative estimate assumes about 4.5 admin hours per device per year that automated provisioning and remote management can take over.
Lawful Finance & Hardware Control Positioning
HeliumMDM provides secure device-control technology for leased, rented, or hire-purchase hardware through authorized enterprise partners. Helium Enterprises Private Limited is a technology provider, not an NBFC or lender. All financial credit and lending operations must be conducted by licensed external institutions, governed by transparent contracts, written customer consent, data privacy standards, and legitimate grievance redressal mechanisms.
HeliumMDM Frequently Asked Questions
Request a Live HeliumMDM Demonstration
Speak directly with our technical team to see live QR enrollment, policy control, and fleet dashboards.